Customer story · Education
Florida Southern College Modernizes IT and Achieves Compliance with Thrive
Florida Southern College, a small private institution, used Thrive risk assessments, on-premise Cloud, DRaaS and DPaaS with immutable backups to reach GLBA and FERPA compliance, with only two minor findings in its 2024 audit.
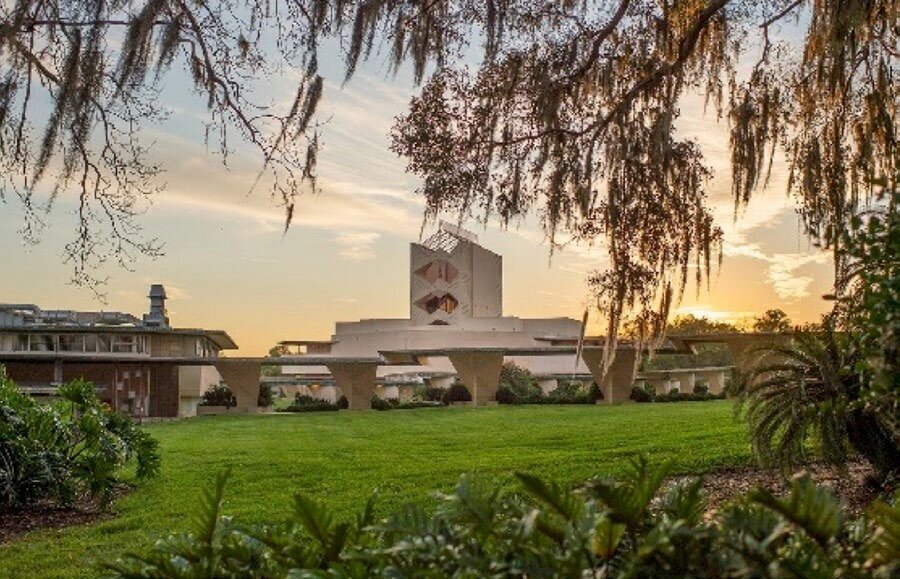
About Florida Southern College
Florida Southern College is a small private institution with a small internal IT team and limited resources. Chief Information Officer Francine Neiling leads its technology function. The college must meet strict regulatory requirements, including the Gramm-Leach-Bliley Act (GLBA) and FERPA, while modernizing infrastructure within tight budget constraints. It originally relied on DSM for disaster recovery and data protection services; Thrive later acquired DSM and became the college's primary security and compliance partner.
The challenge
Florida Southern College faced the dual challenge of modernizing its IT infrastructure and meeting strict regulatory requirements, including the Gramm-Leach-Bliley Act (GLBA) and FERPA, with limited resources and a small internal IT team.
Its network infrastructure was a mix of multiple vendors' equipment, which had previously led to campus-wide outages. Student information had to be secured, data loss prevention improved and multi-factor authentication deployed. The college also needed disaster recovery and data protection that would satisfy auditors and keep critical data recoverable.
CIO Francine Neiling recognized that the college needed continuous risk assessments to identify and remediate vulnerabilities, and that projects had to be prioritized by risk to fit the budget. The college had initially relied on DSM for disaster recovery and data protection; after Thrive acquired DSM, the relationship shifted toward proactive IT improvement and compliance.
Since partnering with Thrive, our security has improved dramatically. What would have taken us years to accomplish on our own was completed efficiently with their hands-on support. They've truly become an extension of our IT team.
The solution
Florida Southern initially engaged Thrive for specific projects, such as migrating student emails to the Cloud. As the college's needs grew, Thrive became its primary partner for security and compliance.
Thrive's cyber risk assessments gave the college detailed insight into gaps and risks, allowing it to allocate resources strategically and prioritize projects based on risk while staying within budget. Neiling noted that where other vendors delivered the basics, Thrive followed up with solutions and guidance to make everything work across the college's systems. Thrive provides regular network assessments and annual penetration tests, with quarterly autonomous pen testing and vulnerability scanning listed among the services, to maintain compliance and security.
For infrastructure, Thrive delivered a fully managed on-premise Cloud with scalable Disaster Recovery as a Service (DRaaS) and Data Protection as a Service (DPaaS), featuring immutable backups with cloud copy and orchestrated offsite recovery. Thrive was also instrumental in deploying multi-factor authentication, improving data loss prevention and securing student information, and it provides email and collaboration security and 24/7 server support with patch management.
The document lists the services as Cyber Risk Assessment, Quarterly Autonomous Pen Testing, On-Premise Cloud, DRaaS, DPaaS with immutable backups and cloud copy, Email & Collaboration Security, 24/7 Server Support with Patch Management, Multi-factor Authentication and Vulnerability Scanning.
The results
- Achieved Gramm-Leach-Bliley Act (GLBA) and FERPA compliance with Thrive's guidance
- Only two minor findings in the college's 2024 audit, reflecting a stronger security posture
- Streamlined network infrastructure resolved multi-vendor equipment issues that had caused campus-wide outages
- Immutable backups and orchestrated offsite recovery keep data secure and recoverable
- Multi-factor authentication deployed and data loss prevention improved to secure student information
- Compliance work saves time and money, letting the small IT team focus on daily operations
Get the full case study
Download the original document as published by Thrive (Thrive Networks) (PDF, 302.0 KB).
More customer stories
Results from similar engagements
Thrive (Thrive Networks) · Financial Services
Zeus Capital validates its cyber defences with Thrive risk assessment
Read more
Thrive (Thrive Networks) · Hospitality & Travel
Wilson Vale moves disaster recovery to the cloud with Thrive support
Read more
Thrive (Thrive Networks) · Financial Services
Vida Bank secures its Azure migration with Thrive managed networking
Read moreYour story could be next
Want results like these?
Every result on this page started with one conversation — let's have yours.